7 Documents to Collect Before Hiring a Crypto Investigator
Gathering key financial records, transaction hashes, and communication logs before hiring a crypto investigator speeds up analysis and strengthens legal cases.
Why Preparing Your Evidence Record Matters
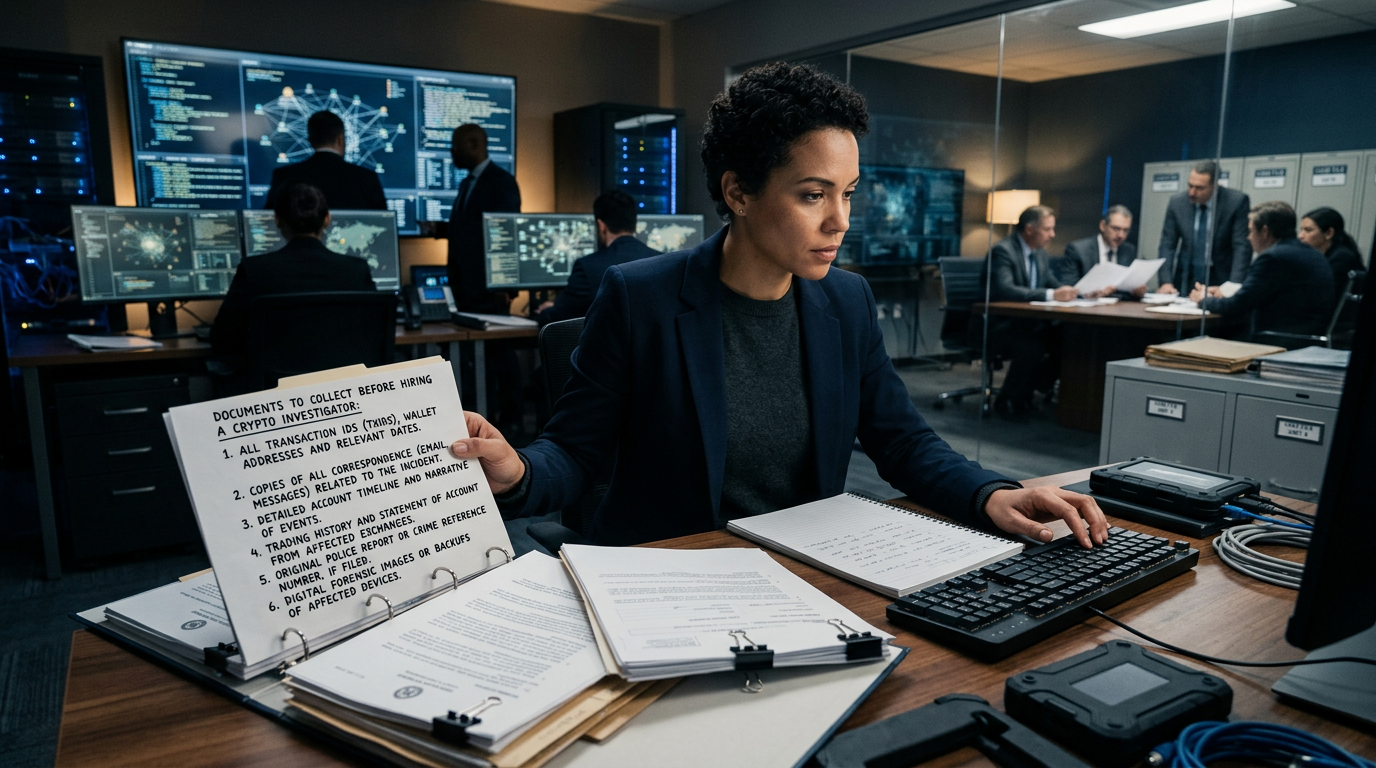
When responding to digital asset theft, speed and clarity are paramount. Knowing exactly which documents to collect before hiring a crypto investigator streamlines the forensic intake process, reduces legal billable hours, and prevents critical digital evidence from being overwritten or lost. Before engaging specialized analysis, organizing your documentation allows forensic investigators to immediately map wallet clusters and coordinate with legal counsel. Learn more about structural tracing procedures in our master guide on tracing funds after a cryptocurrency scam.
Key Documents to Collect Before Hiring a Crypto Investigator
To establish a clear evidentiary trail that satisfies both law enforcement agencies and judicial standards, assemble the following seven categories of documentation prior to retaining a forensic team.
1. Transaction Hashes (TXIDs) and Blockchain Wallet Addresses
The single most critical piece of evidence in any blockchain investigation is the raw on-chain record. A transaction hash (TXID) is a unique alphanumeric string that acts as a digital fingerprint for a specific transaction on a public ledger like Ethereum, Bitcoin, or TRON.
Concrete Example: You transferred 50,000 USDT from a personal wallet to an automated yield platform that turned out to be a fraudulent scheme. Without the specific TXID, forensic teams must manually parse hundreds of transactions across historical timestamps, increasing cost and response latency.
What to do: Copy every outgoing transaction hash from your wallet application or exchange withdrawal history. Ensure you record the exact sending address, the receiving address, the token type, and the precise timestamp down to the second. Avoid relying on screenshots alone for long hash strings, as typographic errors can stall tracing efforts; maintain a plain-text document containing copy-pasted hexadecimal strings.
2. Fiat On-Ramp and Exchange Deposit/Withdrawal Statements
Tracing does not begin and end on the blockchain. Establishing the source of funds through traditional financial channels proves ownership, value, and standing in court proceedings.
Concrete Example: You converted USD into USDC via a regulated exchange like Coinbase or Kraken before transferring the tokens to a fraudulent investment portal. The original fiat deposit receipt links your legal identity to the initial cryptocurrency purchases.
What to do: Download official PDF account statements, deposit receipts, and wire transfer confirmations from your bank and centralized exchange accounts. Ensure these documents show your legal name, account numbers, timestamps, transaction reference numbers, and the precise fiat amounts converted. Reviewing these records alongside early incident response strategies detailed in our guide on critical response steps during the first 72 hours of crypto recovery ensures all primary entry points are accounted for.
3. Complete, Unedited Communications Logs
Fraud perpetrators often rely on social engineering, targeted messaging apps, or deceptive investment portals. Preserving the context and text of these interactions helps establish fraud, intent, and misrepresentation under civil and criminal law.
Concrete Example: An individual posing as an institutional broker convinced you via Telegram or WhatsApp to deposit assets into a bogus liquidity pool, promising guaranteed daily yields.
What to do: Export full, unedited chat transcripts from platforms like Telegram, WhatsApp, Discord, or email clients. Do not rely solely on mobile screenshots, as chats can be remotely deleted by the counterparty. On Telegram, use the desktop application to export full JSON or HTML chat histories including media files. Capture complete email headers (e.g., "Show Original" in Gmail) to preserve sending server IP addresses and routing details.
4. Platform Screenshots, URLs, and Domain Headers
Fraudulent websites, decentralized applications (dApps), and trading dashboards are frequently taken offline by perpetrators as soon as illicit capital is drained or reported.
Concrete Example: You interacted with a smart contract on a domain that mirrored a legitimate decentralized exchange, which contained a hidden drainer script designed to approve unlimited token allowances.
What to do: Take high-resolution, full-page screenshots of all web interfaces, deposit dashboards, balance displays, and error screens before the operators alter or shut down the domain. Record the exact domain URLs, subdomains, and referral links. If comfortable, save web page source codes (HTML) or archive the domain using tools like the Wayback Machine or Archive.today to capture server-side artifacts that can be subpoenaed later.
5. Police Reports and Agency Incident Reference Numbers
While private investigators conduct technical tracing, formal asset preservation orders and exchange subpoenas require authorization from law enforcement or judicial bodies.
Concrete Example: Forensic analysis traces stolen assets directly to a deposit account at a major regulated exchange. The exchange will not freeze assets or disclose Know Your Customer (KYC) identity data without an active law enforcement request, court order, or formal legal process.
What to do: File a formal report with local law enforcement and federal reporting portals such as the FBI’s Internet Crime Complaint Center (IC3). Keep exact copies of the submitted crime report, law enforcement agency case numbers, and the contact details of assigned detectives or agents. Victims undergoing crypto recovery in Colorado or other state jurisdictions should ensure their police reports explicitly cite cryptocurrency wallet addresses and approximate fiat equivalencies at the time of transfer.
6. Account Ownership and KYC Verification Records
To reclaim frozen funds or submit formal legal claims against fraudulent entities, you must prove that the compromised originating account or wallet legally belonged to you.
Concrete Example: A centralized exchange successfully freezes funds tied to an exploit but requires proof that the victim seeking restitution is the rightful owner of the originating wallet.
What to do: Gather government-issued identification used to open exchange accounts, proof of address utility bills, and profile screenshots showing verified KYC status from the exchange used to purchase the initial assets. Maintain these in a secure, encrypted folder ready for legal discovery.
7. Technical Logs and Wallet Configuration Artifacts
When dealing with compromised self-custody wallets or smart contract exploits, technical logs reveal the precise vector of compromise.
Concrete Example: A malicious browser extension or malicious approval transaction drained your wallet without exposing your seed phrase directly.
What to do: Document the wallet provider (e.g., MetaMask, Ledger, Trust Wallet), version numbers, connected dApp approvals, and browser extension logs. Do not input or share your seed phrase or private key with anyone, including private forensic investigators. Legitimate firms only require public addresses and transaction hashes to complete complete on-chain analysis. To understand how these technical inputs are analyzed, review our overview on understanding blockchain forensic evidence standards and limitations.
Frequently Asked Questions About Evidence Collection
What is the single most critical document needed for a crypto fraud investigation?
Transaction hashes (TXIDs) and destination wallet addresses are the most critical data points. They allow forensic analysts to immediately query immutable blockchain ledgers, identify asset flows, locate intermediate hops, and isolate potential centralized exchange deposit endpoints where funds can be subpoenaed or frozen.
Do I need a formal police report before hiring a private blockchain investigator?
While a police report is not strictly required to initiate preliminary blockchain tracing, obtaining an official crime report number from law enforcement is necessary before formal subpoenas or court-ordered asset freezing applications can be executed by legal counsel.
How do web screenshots and technical headers assist in asset tracing?
Web headers and unedited site captures contain raw IP addresses, domain names, server timestamps, and browser routing data. This metadata enables investigators and legal teams to issue targeted subpoenas to domain registrars and web hosting providers to identify platform operators.
What to Do If You Have Collected These Documents
Once you have compiled these essential records, avoid sharing sensitive documents on public forums or unverified Telegram channels. Be aware that asset recovery scams heavily target victims of financial fraud; unsolicited messages offering guaranteed fund recovery or claiming direct backdoor access to blockchain ledgers are fraudulent.
Blockchain intelligence agencies provide forensic analysis that supports legal counsel in seeking civil injunctive relief or aiding law enforcement actions. To understand how these records translate into courtroom evidence, read our analysis on how forensic reports support crypto recovery in court proceedings. If stolen assets are traced to major stablecoins, formal reports may support administrative freeze applications, as detailed in our analysis of USDT freeze requests and stablecoin recovery processes.
Related Reading in This Series
- How to Recover Scammed Cryptocurrency: First 72 Hours
- Blockchain Forensics: What It Proves and Its Real Limits
- How to Report a Crypto Scam in the US: Step-by-Step Guide
What to Do Next
If you have organized your transaction history and communication logs, the next step is a formal, confidential review of your case evidence. Aegis Financial Forensics provides objective, legally defensible blockchain tracing reports suitable for law enforcement submission and court filings.
Contact our investigative team today via our confidential portal at /contact to discuss your documentation. Learn more about our technical evidentiary standards by reviewing our complete forensic analysis standards at /methodology.